LIVE
BREAKING
Lapid Accuses Netanyahu of Attempted Coup Over Election-Day Action Against Arab PartiesHouthis Blame Saudi Arabia for Strikes That Killed Three, Including a Child, in YemenMore Than 50 Countries Back COP31 Geothermal Ambition 2050Ukraine Strikes Ilsky Oil Refinery in Southern RussiaEngland End Spain’s 43-Match Unbeaten Run With Famous 3-2 Win in MadridFrance and Britain to Host Paris Conference on Russia’s Shadow FleetEU Accuses Russia of Stalling Ukraine Peace Talks to Target Power Plants as Winter NearsCOP31 Final Week Opens as Ministers Take Over the Fight for a Deal in AntalyaRescue Ships Rush to Sinking Cargo Vessel in Black Sea as 12 Crew Unaccounted ForHoungbo Re-elected to Lead UN Labour Agency for Second TermClimate Ambassadors at COP31: Who They Are and What They Do in AntalyaTanker Struck by Unknown Projectile in Strait of Hormuz, Engine Room Catches FireUkraine Hits Crimean Bridge, Traffic Curbed Across Kerch StraitUN Climate Chief at COP31: Blunt AI’s Dangerous Edges, Put It Responsibly to WorkSadiq Khan Warns World Leaders at COP31: Climate Disinformation Threatens Planet and DemocracyCyclone Akvan to Strike Andhra Pradesh Coast as Very Severe Storm on 20 NovemberECO Foreign Ministers Meet in Islamabad to Adopt Vision 2035Parliamentarians Take Centre Stage at COP31 as Lawmakers Gather in Antalya and Launch New Climate GuideCOP31 First Week Ends With Clear Momentum for Concrete Action, Presidency SaysCOP31: Tech Giants Back Antalya AI Pledge as Presidency Launches AI and Green Industry PackageLapid Accuses Netanyahu of Attempted Coup Over Election-Day Action Against Arab PartiesHouthis Blame Saudi Arabia for Strikes That Killed Three, Including a Child, in YemenMore Than 50 Countries Back COP31 Geothermal Ambition 2050Ukraine Strikes Ilsky Oil Refinery in Southern RussiaEngland End Spain’s 43-Match Unbeaten Run With Famous 3-2 Win in MadridFrance and Britain to Host Paris Conference on Russia’s Shadow FleetEU Accuses Russia of Stalling Ukraine Peace Talks to Target Power Plants as Winter NearsCOP31 Final Week Opens as Ministers Take Over the Fight for a Deal in AntalyaRescue Ships Rush to Sinking Cargo Vessel in Black Sea as 12 Crew Unaccounted ForHoungbo Re-elected to Lead UN Labour Agency for Second TermClimate Ambassadors at COP31: Who They Are and What They Do in AntalyaTanker Struck by Unknown Projectile in Strait of Hormuz, Engine Room Catches FireUkraine Hits Crimean Bridge, Traffic Curbed Across Kerch StraitUN Climate Chief at COP31: Blunt AI’s Dangerous Edges, Put It Responsibly to WorkSadiq Khan Warns World Leaders at COP31: Climate Disinformation Threatens Planet and DemocracyCyclone Akvan to Strike Andhra Pradesh Coast as Very Severe Storm on 20 NovemberECO Foreign Ministers Meet in Islamabad to Adopt Vision 2035Parliamentarians Take Centre Stage at COP31 as Lawmakers Gather in Antalya and Launch New Climate GuideCOP31 First Week Ends With Clear Momentum for Concrete Action, Presidency SaysCOP31: Tech Giants Back Antalya AI Pledge as Presidency Launches AI and Green Industry Package
Security

Patch Now: PHP Flaws Exploited in the Wild as Stolen Microsoft Tokens Hit 79 Organisations

News Desk 2Published October 26, 2026
Patch Now: PHP Flaws Exploited in the Wild as Stolen Microsoft Tokens Hit 79 Organisations
Share this story

Security teams are starting the week with two urgent warnings: PHP flaws patched less than a week ago are already being exploited in the wild, and a campaign that replayed stolen Microsoft 365 session tokens reached email accounts at 79 organisations. The advice from researchers is blunt — patch PHP now, and revoke sessions rather than assuming a password change is enough.

FAKTA

  • PHP2Shell flaws: CVE-2026-109618 and CVE-2026-109619, rated CVSS 9.2, patched on 21 October 2026.
  • Fixed versions reported: PHP 8.5.12, 8.4.27, 8.3.36 and 8.2.35, with workers fully restarted after upgrading.
  • Scanning reported: 216 internet-facing hosts compiled as apparently unpatched or only partly mitigated.
  • Microsoft 365 campaign: 497 sign-ins counted across 79 organisations, using replayed session tokens.
  • Separate PHP flaw: CVE-2026-115560, with no patch reported, mitigated by setting session.upload_progress.enabled=0.

PHP security patch: what is being exploited

The PHP flaws, known as PHP2Shell, allow remote code execution — meaning an attacker who can reach a vulnerable server may be able to run their own commands on it. Researchers at Cyfirma, cited in Monday’s cyber briefings, reported that operators had compiled a list of 216 internet-facing hosts that still appeared unpatched or only partly mitigated for the two flaws, and were probing them from compromised scan nodes.

The reported targets span government, banks, logistics, airports, manufacturing and online transaction platforms. The briefings describe the operators as Korean-speaking and link the scanning to a suspected North Korean campaign; that attribution is reported by the researchers, not independently confirmed here.

Patching means upgrading to one of the fixed versions — 8.5.12, 8.4.27, 8.3.36 or 8.2.35, depending on the branch in use — and fully restarting the workers afterwards. An upgrade without a restart may leave vulnerable processes running.

Stolen tokens bypass passwords and checks

The second warning concerns Microsoft 365. Security firm Huntress, cited in the same briefings, described a campaign that replayed stolen session tokens for weeks to reach email accounts at 79 organisations, bypassing multi-factor authentication. In total, 497 sign-ins were counted.

The lesson matters because a session token represents a login that has already passed verification. If it is stolen, an attacker may not need the password or the second factor at all. Defenders are advised to revoke sessions, remove rogue devices and unauthorised multi-factor methods, and hunt for sign-ins that do not match the user’s normal pattern.
PHP security patch — cybersecurity operations centre

File photo: a cybersecurity operations environment. It does not depict the specific systems named in this report.

One more PHP flaw, and what to do first

Briefings also flag a newer PHP flaw, CVE-2026-115560, for which no patch was reported on Monday. The interim mitigation given is to set session.upload_progress.enabled=0. Organisations should treat that as a temporary control, not a substitute for the patched versions above.

In practical order: first, inventory every internet-facing PHP host and confirm its version; second, upgrade and restart; third, review Microsoft 365 sign-ins and revoke any session that cannot be explained; fourth, check for unexpected devices or authentication methods added to accounts.

Related Articles

Conclusion

Both warnings point in the same direction: the fastest risks this week are not exotic new techniques but known flaws left unpatched and valid sessions left unrevoked. Closing those two gaps first gives defenders the most protection for the least delay.
Frequently Asked Questions

Related Stories

Planet & environment

Climate & Sustainability

News, stories and solutions driving change towards a greener and more sustainable planet for future generations.

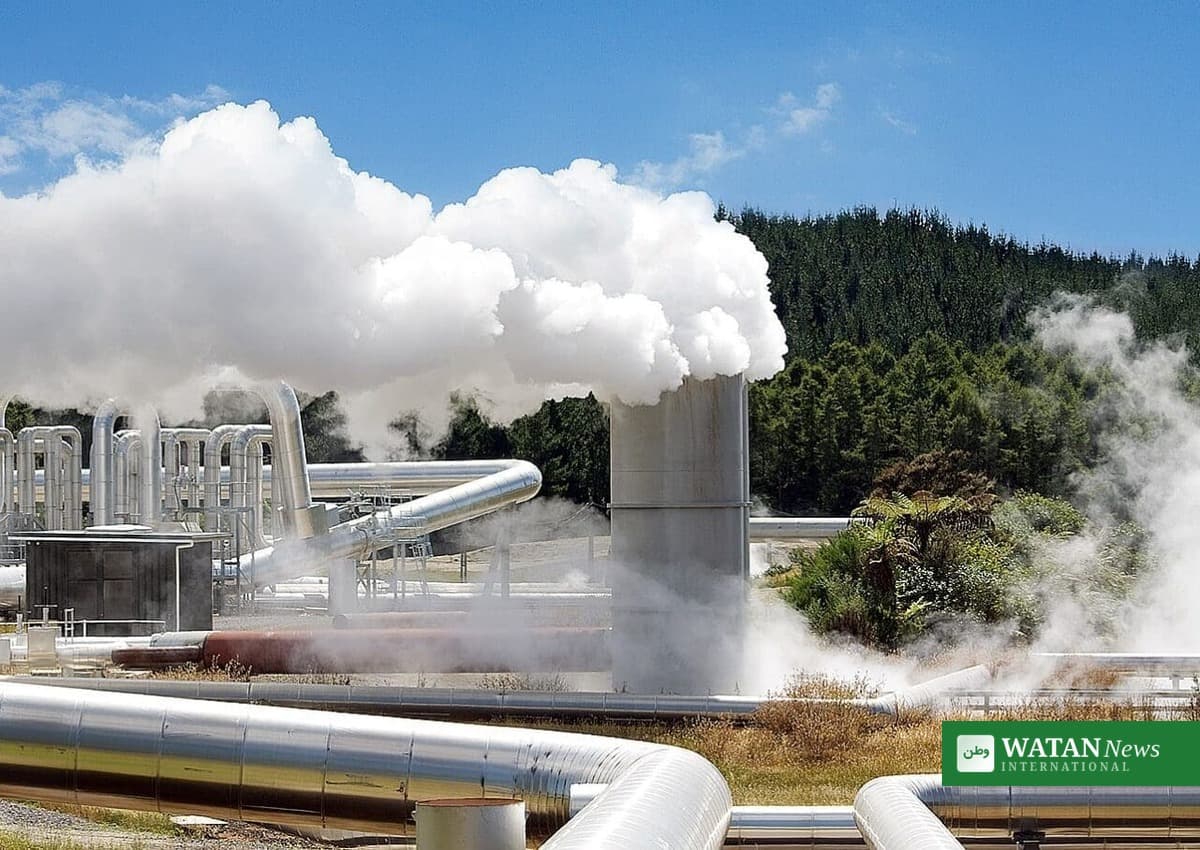
More Than 50 Countries Back COP31 Geothermal Ambition 2050
Featured story

More Than 50 Countries Back COP31 Geothermal Ambition 2050

More than 50 countries have backed the COP31 Global Geothermal Ambition 2050, the COP31 Presidency said on 16 November — a collective goal to scale geothermal power and heat to 12 times 2025 levels by 2050, with IRENA and the EU behind the delivery plan.

Read full story

GREEN JOURNALISM

Every Action Counts

Small steps today, big impact tomorrow.

Explore more stories