Two critical security flaws in PHP, the programming language behind a large share of the internet, forced government websites in Europe offline on Wednesday as emergency patches were released. The flaws, nicknamed PHP2Shell, allow an attacker to run code on a web server without logging in, and developers and governments alike urged website operators to update immediately.
PHP released fixed versions on Wednesday, October 21, at 14:00 UTC, a day earlier than planned, after details of the flaws leaked. The US cybersecurity agency CISA issued an urgent alert the same day, and the White House said it was working to speed the fix out to users and protect American networks and critical infrastructure.
FAKTA
- Flaws: CVE-2026-109618 and CVE-2026-109619, jointly nicknamed PHP2Shell
- Severity: 9.2 out of 10 on the CVSS v4.0 scale for each flaw
- Risk: Unauthenticated remote code execution on PHP installations serving web requests
- Fixed versions: PHP 8.5.12, 8.4.27, 8.3.36 and 8.2.35, released on October 21, 2026
- Reach: PHP runs nearly 70 percent of websites whose programming language can be identified, and powers WordPress, which runs about 40 percent of all websites
- Official advice: Update immediately; systems that cannot be updated should be taken offline until they can be patched
PHP2Shell critical flaw: what went wrong
The PHP2Shell critical flaw is not a bug in a single website, plugin or app. It sits in PHP itself, the software running underneath websites, so a carefully secured site can still be exposed through the PHP version its server runs. According to the PHP security advisories, one flaw lets out-of-memory handling corrupt a request that is only partly set up, while the other lets request data survive after its memory is freed, so a later request handled by the same worker can read the stale state.
The PHP team described the risk as highest for servers running Apache with mod_php, where a demonstrated exploit lets an unauthenticated request trigger the attack before any website code runs. PHP-FPM, php-cgi, FrankenPHP and LiteSpeed deployments are also at risk. Security researchers said there is no generic configuration change that fully fixes the problem: updating is the only complete remedy, although a web application firewall can offer partial protection in the meantime.
Government websites taken offline as a precaution
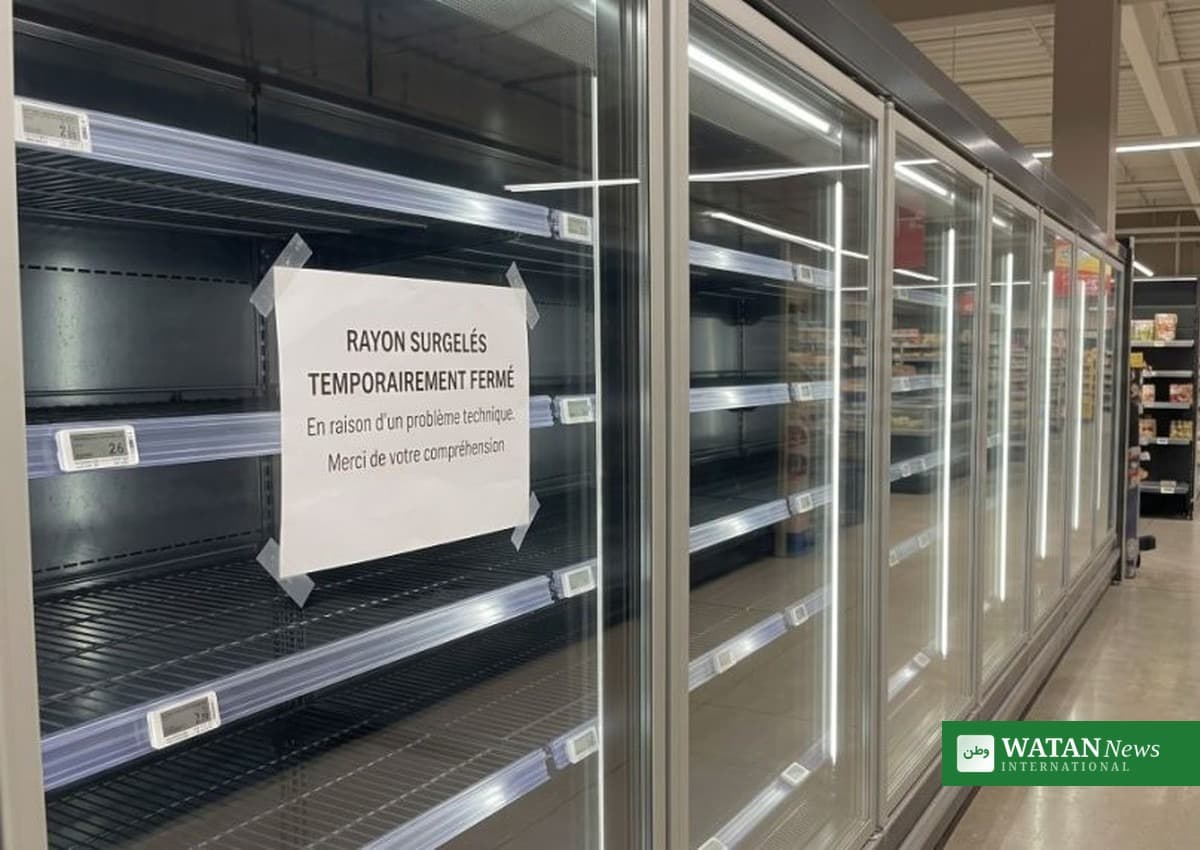
Several government, school and hospital websites in Europe were taken offline on Wednesday as operators raced to protect themselves. The Dutch government was among those that took sites offline as a precaution, and Germany’s federal IT service provider, ITZBund, temporarily deactivated several websites, saying the move was purely preventive and that no security incidents were known to have occurred.
The European Union’s cybersecurity response team, CERT-EU, had warned that organisations unable to apply the fixes in time should consider taking affected sites offline. The US National Security Agency gave similar advice, urging organisations using PHP to be prepared for the update and to take systems offline until fully mitigated if they could not update immediately.
Patches land a day early after details leak
The coordinated disclosure had originally been planned for October 22, but details of the two flaws leaked on October 20, forcing an accelerated release. The PHP developers published the fixed versions on Wednesday afternoon UTC and strongly encouraged users to update immediately. Organisations using Linux distributions or long-term support services were told to check their vendors for updated packages, including fixes adapted for older versions.
PHP 8.1 and older branches receive no official fixed release, although the PHP team published source backports for versions 7.4, 8.0 and 8.1 for vendors to adapt. Cloudflare, which filters web traffic for many sites, said it was seeing early attack attempts and switched on firewall rules as a stopgap, while CISA said it had not observed exploitation at the time of its alert and Australia’s cyber agency said it was not aware of active exploitation.
What website owners should do now
CISA urged organisations to inventory every system running PHP, apply the patch immediately with internet-facing systems first, and watch for suspicious activity such as PHP worker processes launching shells or downloading tools. Organisations that cannot update right away, or that still run PHP 8.1 or earlier, should take their PHP-based systems offline until they can be patched or updated.
The White House said the flaw was discovered with the help of artificial intelligence technology and that the administration, notified on October 16, was working with federal agencies and AI companies to expedite the release of the fix. For ordinary visitors, the flaw is a server-side problem: simply visiting a website does not put a personal computer or phone at risk, but site owners were warned to expect fake mirror links and bogus patch downloads exploiting the confusion.
More coverage of major technology stories can be found in Watan News International’s technology news section.